Gemini 3.8 Flash Cyber is a security-tuned variant of Gemini 3.8 Flash that Google released on September 2, 2026, the same day as the general-purpose model. You can’t sign up for it. Access runs through a new vetting scheme called the Fairwind Program, aimed at government authorities, critical infrastructure operators, software maintainers, and core technology platforms. There’s no public API, no published price, and no self-hosting option, because the weights stay closed.
That makes this a different kind of article from the rest of the Gemini 3.8 Flash series. There’s no curl command to paste and no cost table to argue over. What’s worth understanding is what the model does, who Google trusts with it, what the vetted partners have to promise, and what the published results say about its ability to find and patch vulnerabilities. Google’s launch post and the Fairwind Program page are the primary sources for everything below.
The last section is for everyone else. If you build APIs and you don’t run a national CERT, the model you can use today is plain Gemini 3.8 Flash, and the security work you can do today is the routine kind: auth checks, negative tests, and scheduled regression runs. That’s where Apidog fits, and this guide is clear about what it does and doesn’t cover.
Gemini 3.8 Flash Cyber at a glance
| Item | Value |
|---|---|
| Announced | September 2, 2026, alongside Gemini 3.8 Flash |
| Base model | Gemini 3.8 Flash (model card: “based on Gemini 3.7 Flash”) |
| Purpose | Vulnerability discovery, patching, and defensive security workflows |
| Access | Fairwind Program only: application, background checks, contractual obligations |
| Eligible groups | Trusted government authorities, critical infrastructure operators, software maintainers, core technology platforms; academic labs doing defensive benchmarking may apply |
| Public API | None |
| Public pricing | None |
| Self-hosting | Not possible; weights are closed |
| Predecessor | Gemini 3.5 Flash Cyber limited pilot (July 2026, governments and trusted partners) |
| Ships with | CodeMender integration for automated fixes |
| Model you can use instead | gemini-3.8-flash through the Gemini API and Google AI Studio |
What Gemini 3.8 Flash Cyber is
Think of it as Gemini 3.8 Flash with the safety envelope changed, not a separate model line. MarkTechPost described the pair as “one core model, two access envelopes,” and that framing holds up against Google’s own materials. The general model carries the standard safety training that pushes back on offensive-security requests. The Cyber variant is tuned to work through them: read a codebase, hunt for an exploitable bug, reason about how it could be triggered, and propose a patch.
That capability cuts both ways, which is why Google won’t put it behind a public key. The same model that helps the Chrome security team fix bugs faster would help an attacker find them faster. Google’s answer is to keep the model server-side, hand access only to vetted defenders, and attach contractual strings to every seat.
Two practical consequences follow. First, everything you read about 3.8 Flash Cyber’s performance comes from Google or from named partners in Google’s post. No independent lab has a key. Second, the “3.8” in the name tells you the underlying reasoning and coding capability. If you want a sense of how the base model behaves on long-horizon agent tasks, the 3.8 Flash API guide covers the Interactions API, thinking levels, and the token budget the “works harder” design consumes.
The Fairwind Program: who gets access
The Fairwind Program is the new front door. It replaces the invitation-only arrangement that governed the 3.5 Flash Cyber pilot with a documented application process and a fixed set of obligations.
Who can apply
Google lists four partner categories: trusted government authorities, critical infrastructure operators, software maintainers, and core technology platforms. Academic labs doing defensive benchmarking may also apply. Every applicant goes through a background check that looks at security history and what Google calls “ethical operations.” The bar is meant to exclude anyone who could turn the model outward.
Notice what’s missing from that list. Independent security researchers, bug bounty hunters, consultancies, and SaaS companies without an infrastructure or platform footprint don’t appear. The published categories don’t invite them.
What partners must commit to
Approval isn’t the end of the process. Fairwind partners take on a set of operating obligations:
- User-level authentication for every person who touches the model, backed by phishing-resistant MFA and access controls.
- Access limited to internal cybersecurity, incident response, and penetration testing teams. Product teams and general engineering don’t qualify.
- Tracking of which employees have access and how they use it.
- No sharing, redistribution, or resale of access under any arrangement.
The last point closes the obvious loophole. A partner can’t wrap the model in a service and sell it onward, and it can’t lend a key to a contractor. If you’re hoping a vendor will resell 3.8 Flash Cyber capability, the program terms rule that out.
What Google says the results show
Every figure here is either Google-run or reported by a partner in Google’s launch materials. Treat them as vendor claims until someone outside the program reproduces them, which the access model makes hard.
| Claim | Source | Result |
|---|---|---|
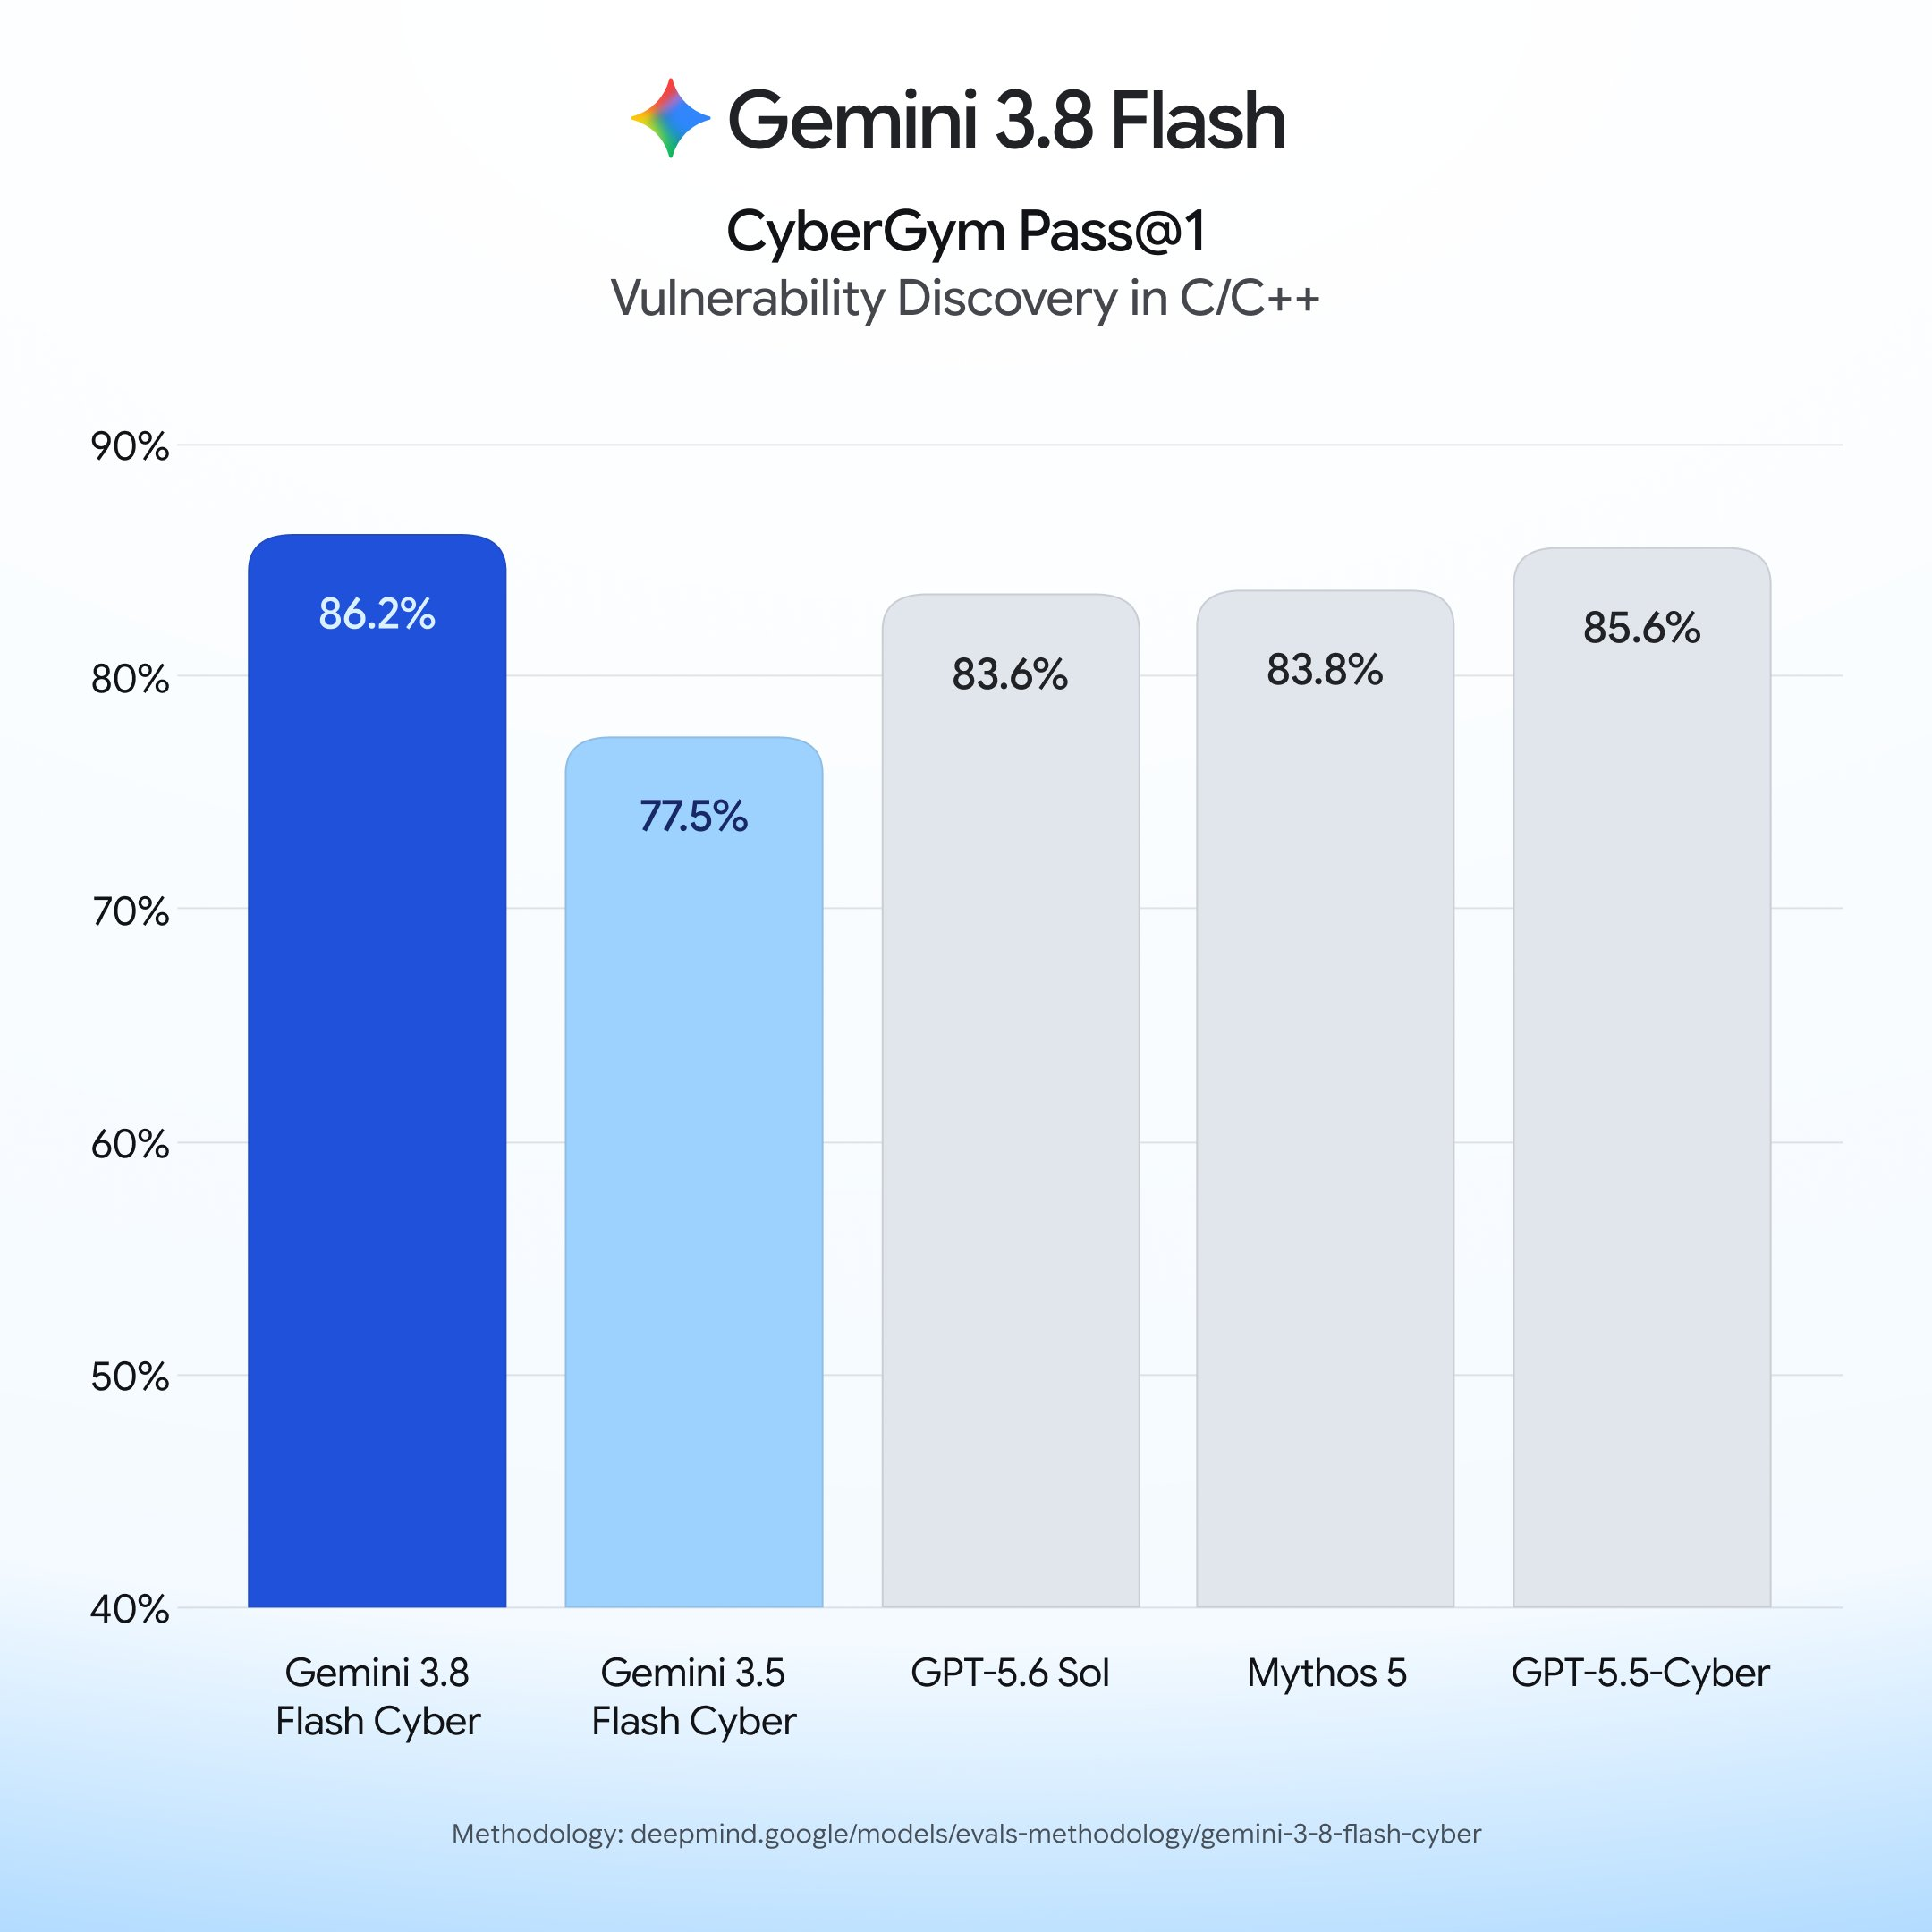
| CyberGym | Surpasses 3.5 Flash Cyber and larger frontier models (no score printed in text) | |
| Real-world vulnerability discovery | Success rate above 70% across 20 programming languages | |
| CWE-Bench patching | 47.2% pass@1, vs 47.8% for the leading frontier model “at higher cost” | |
| Chrome vulnerability patches | Chrome security team | 2.6 times more correct patches than the best commercial models, which are much larger |
| Recall on security findings | Wiz | 7.5 to 9.7 percentage points higher recall at 2.3x to 5.2x lower cost |
| Time to find a critical vulnerability | Google Cloud Vulnerability Research | Under 2 hours, versus months previously |
A few notes on reading that table. The CWE-Bench line is the most candid one Google publishes: 47.2% sits slightly below the 47.8% of the unnamed leader, and Google’s argument is cost, not raw accuracy. That matches the whole Flash positioning. The Chrome and Wiz numbers are comparisons against “much larger” commercial models, which suggests the benefit is getting frontier-adjacent security results from a Flash-sized model. The two-hour figure is a single anecdote from one internal team, not a benchmark.
The CodeMender integration matters for how partners use it. CodeMender is Google’s automated fix tooling, and 3.8 Flash Cyber ships wired into it, so a discovered vulnerability can flow straight into a proposed patch instead of stopping at a report.
Google hasn’t published a safety breakdown specific to the Cyber variant. The DeepMind model card covers the base 3.8 Flash and reports small safety deltas against 3.7 Flash: text-to-text safety down 0.4 points, multilingual safety up 5.4 points, unjustified refusals up 1.1 points. Whether those deltas hold on the Cyber tuning isn’t stated.
How it replaces the 3.5 Flash Cyber pilot
Gemini 3.5 Flash Cyber arrived on July 21, 2026, alongside Gemini 3.6 Flash, as a limited pilot for governments and trusted partners. It never had a public surface either. Our 3.5 Flash Cyber explainer covered what was known at the time, and the GPT-5.6 Cyber vs Gemini 3.5 Flash Cyber comparison looked at how the two vendors’ gated security models lined up.
Three changes came with 3.8:
- The base model moved three Flash releases forward. 3.5 Flash Cyber sat on the older 3.5 Flash line. 3.8 Flash Cyber inherits the “works harder” design, the 1,048,576-token context, and the iterative tool-calling behavior of 3.8 Flash, which is the kind of long-horizon work vulnerability hunting demands.
- The pilot became a program. Fairwind formalizes eligibility, background checks, and obligations that were previously handled partner by partner.
- Google published partner results. The 3.8 launch names Chrome, Wiz, and Google Cloud Vulnerability Research and prints figures, even if they’re all Google-sourced.
9to5Google’s launch coverage describes the Cyber model as “replacing version 3.5.” Google hasn’t published a sunset date for existing 3.5 Flash Cyber pilot access or said whether pilot partners move to Fairwind automatically. [VERIFY]
For the wider picture, OpenAI’s GPT-5.6 Cyber occupies the same niche: a security-capable variant with vetted access and no public API. A direct head-to-head between the two isn’t possible without keys to both, and no independent lab has them.
What it means for teams without Fairwind access
Most readers of this blog won’t qualify for Fairwind, and that’s fine. The accessible model is Gemini 3.8 Flash, a capable code reasoner at $0.75 per million input tokens and $3.75 per million output tokens through December 31, 2026, doubling to $1.50 and $7.50 on January 1, 2027. It supports function calling, structured outputs, code execution, and thinking levels of low, medium, and high, all through the Gemini API and Google AI Studio.
What plain 3.8 Flash won’t do is the offensive part. It will review your code, explain a CVE class, and draft a fix for a bug you point it at. Ask it to find exploitable paths through a live target and you’ll hit the general model’s refusals, by design. The 3.8 Flash pricing breakdown covers the token math if you plan to run code review at volume.
The useful takeaway is that the security work most API teams need doesn’t require a gated model at all. The failure modes behind most API incidents are mundane: broken authentication, missing authorization checks, unvalidated input, and endpoints nobody tests after the sprint that shipped them. None of that needs a frontier vulnerability hunter. It needs tests that run on a schedule and fail loudly.
Testing your API’s security posture in Apidog
Apidog is an API client and testing platform, not a vulnerability scanner. It won’t find a memory-safety bug in your service the way 3.8 Flash Cyber found one in Chrome. What it does is verify that your API enforces the rules you wrote, every day, without a human remembering to check. Three patterns cover most of the ground.
Auth checks. For each protected endpoint, build a small test scenario that sends four variants: a valid token, no token, an expired token, and a token with the wrong scope or role. Assert 200 on the first and 401 or 403 on the rest. Store the tokens as environment variables so the scenario runs unchanged across staging and production. This catches the most common API failure, an endpoint that quietly stopped checking authorization after a refactor.
Negative tests. Send what an attacker would send: malformed JSON, oversized payloads, string values where integers are expected, path and query parameters stuffed with injection strings and unicode edge cases. Assert that the API returns a controlled 4xx with a clean error body instead of a 500 with a stack trace. A 500 here means your validation isn’t running, and the stack trace is a gift to whoever sent the request.
Scheduled runs. Wire those scenarios into a schedule so they execute against every environment on a fixed cadence and on each deploy. The scheduled API tests guide walks through the setup. The point is that security regressions get caught on the day they ship, not in a quarterly audit.
If you also use Gemini 3.8 Flash in your stack, the same workspace can hold those requests: send an Interactions API call, assert on the response schema and usageMetadata token counts, and schedule it alongside your security scenarios. Download Apidog to set this up.
FAQ
Can I get API access to Gemini 3.8 Flash Cyber? No. There is no public API, no self-serve signup, and no pricing page. Access goes through the Fairwind Program, which requires an application, background checks, and acceptance of the operating obligations described above. If you meet the eligibility categories, apply through the Fairwind page.
How much does Gemini 3.8 Flash Cyber cost? Google hasn’t published a price. Terms are set within the Fairwind Program and aren’t public. Any figure you see elsewhere is a guess.
Is Gemini 3.8 Flash Cyber a different model from Gemini 3.8 Flash? It shares the core model. The difference is the tuning and the access envelope: the Cyber variant works through offensive-security tasks the general model refuses, and it’s only available to vetted defenders. The Gemini 3.8 Flash pillar covers the base model’s specs and benchmarks.
How does it compare to GPT-5.6 Cyber? Both are gated, both target vulnerability discovery and patching, and neither has a public API. A direct comparison isn’t possible without access to both, and no independent lab has it. The DeepMind Flash page is the place to watch for any further Google-published numbers.
What should I use if I can’t get in? Gemini 3.8 Flash for code review and explanation, paired with routine API security testing: auth checks, negative tests, and scheduled runs. That combination covers the failure modes behind most real API incidents.
Where this leaves you
Gemini 3.8 Flash Cyber is a real capability jump for the defenders Google lets in, and the Fairwind Program is a clearer, stricter gate than the 3.5 pilot it replaces. For everyone outside that gate, nothing about your options changed on September 2. You still have Gemini 3.8 Flash, which you can call today, and you still own the unglamorous work of proving your API rejects bad tokens and bad input. Do that on a schedule, and you’ll catch the class of bug that no gated model would have been pointed at anyway.